Cover of AI Red Team

Book 4 · Presentation

AI Red Team

AI as an Active Part of Cyber Defence in European Enterprises and Public Authorities

69 slidesPowerPoint · 3.5 MB

Download the deck (.pptx) Read the book online

All presentations / AI Red Team

All slides

Select a slide to see it larger; use the arrow keys to move through the deck.
  1. Slide 1: AI Red Team1
  2. Slide 2: Foundations2
  3. Slide 3: Introduction: Putting AI to Work in Cyber Defence3
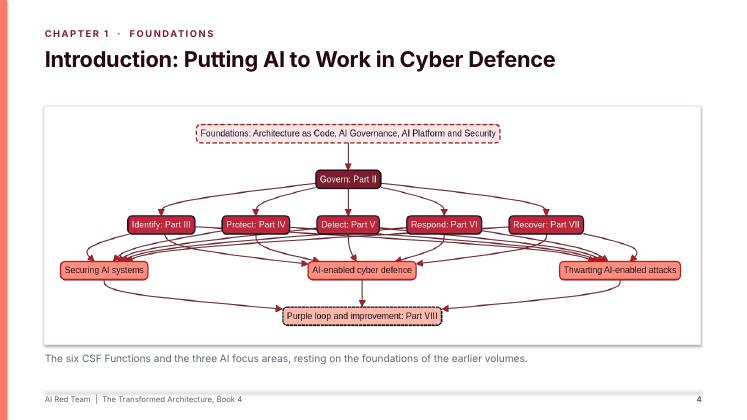
  4. Slide 4: Introduction: Putting AI to Work in Cyber Defence4
  5. Slide 5: The Threat Landscape When Attackers Use AI5
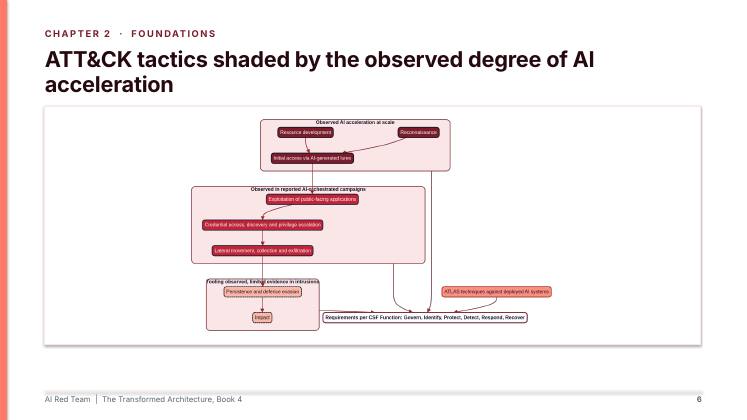
  6. Slide 6: ATT&CK tactics shaded by the observed degree of AI acceleration6
  7. Slide 7: NIST CSF 2.0 with an AI Focus: Functions, Focus Areas and European Obligations7
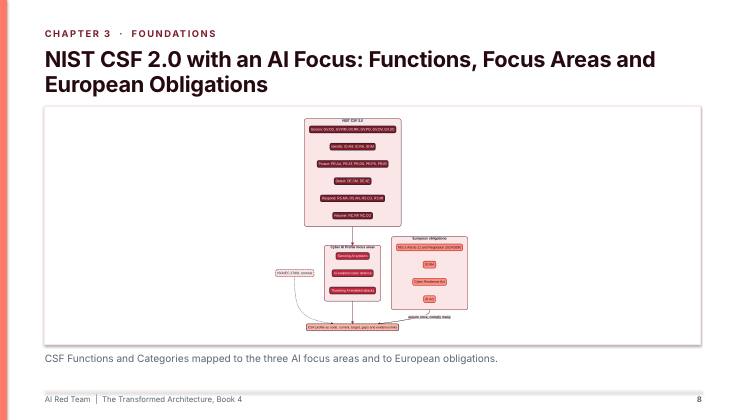
  8. Slide 8: NIST CSF 2.0 with an AI Focus: Functions, Focus Areas and European Obligations8
  9. Slide 9: A Reference Architecture for AI-Enabled Cyber Defence9
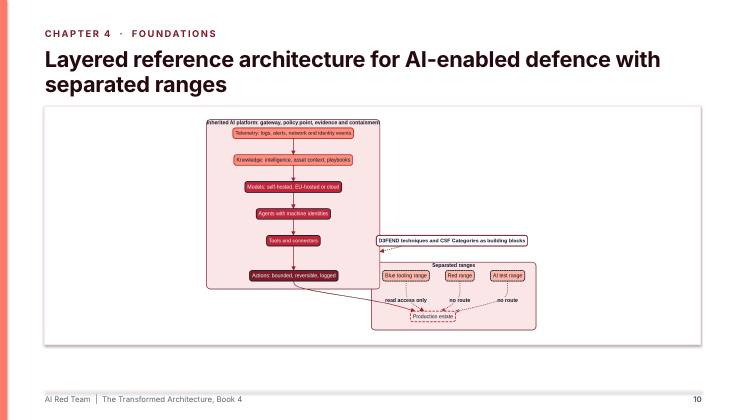
  10. Slide 10: Layered reference architecture for AI-enabled defence with separated ranges10
  11. Slide 11: Govern11
  12. Slide 12: Organisational Context and Risk Strategy for AI in Cyber Defence12
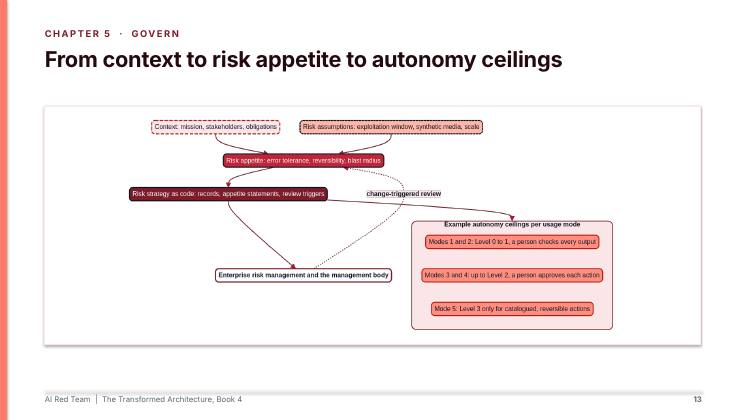
  13. Slide 13: From context to risk appetite to autonomy ceilings13
  14. Slide 14: Roles, Usage Modes and Autonomy Levels: People in Command of Security AI14
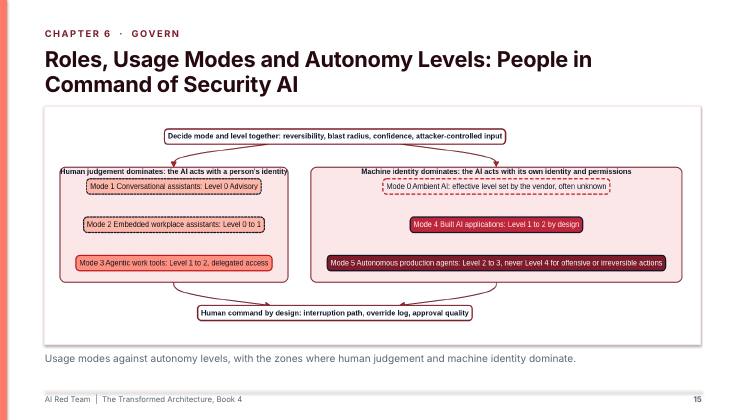
  15. Slide 15: Roles, Usage Modes and Autonomy Levels: People in Command of Security AI15
  16. Slide 16: Policy, Mandate and Rules of Engagement16
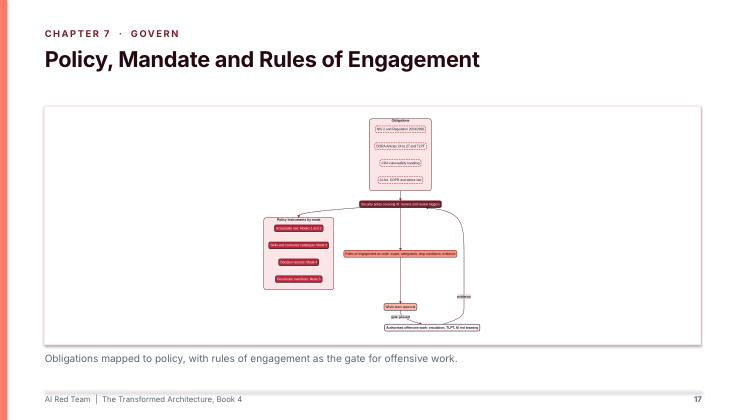
  17. Slide 17: Policy, Mandate and Rules of Engagement17
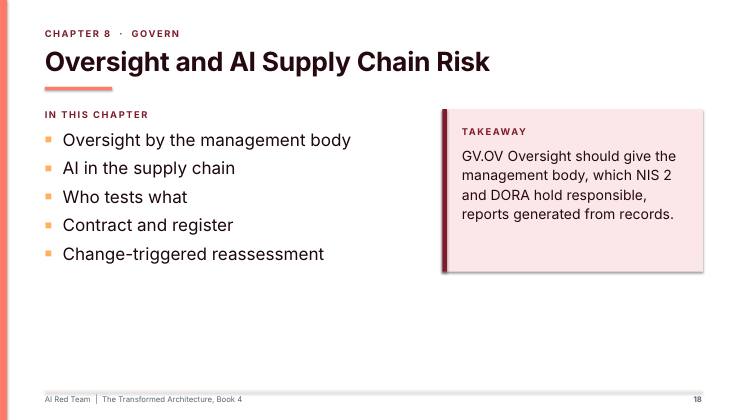
  18. Slide 18: Oversight and AI Supply Chain Risk18
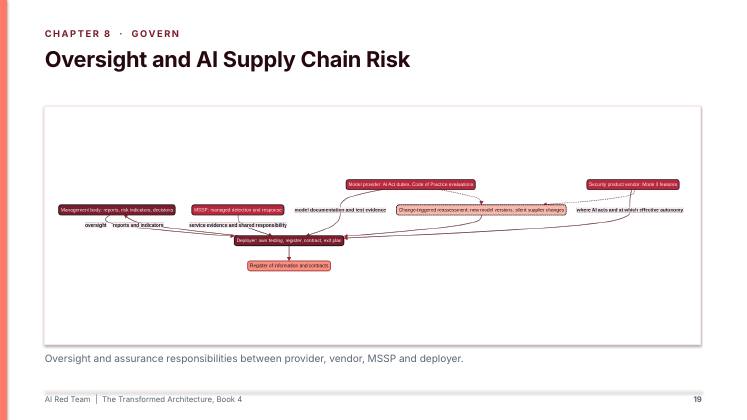
  19. Slide 19: Oversight and AI Supply Chain Risk19
  20. Slide 20: Identify20
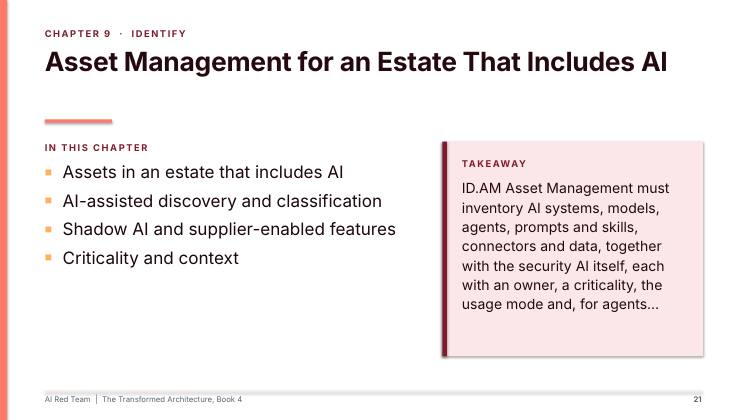
  21. Slide 21: Asset Management for an Estate That Includes AI21
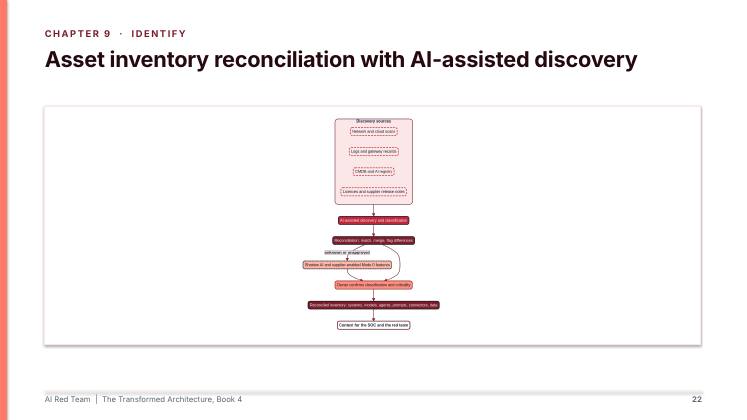
  22. Slide 22: Asset inventory reconciliation with AI-assisted discovery22
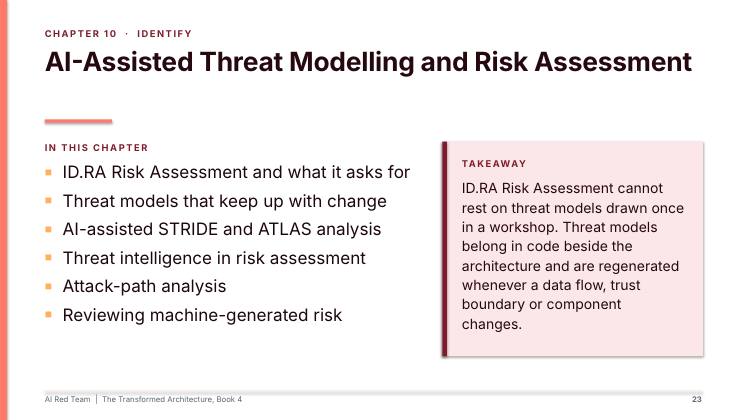
  23. Slide 23: AI-Assisted Threat Modelling and Risk Assessment23
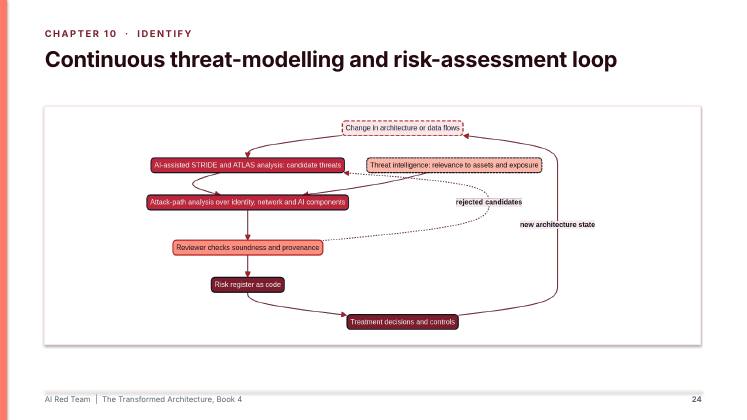
  24. Slide 24: Continuous threat-modelling and risk-assessment loop24
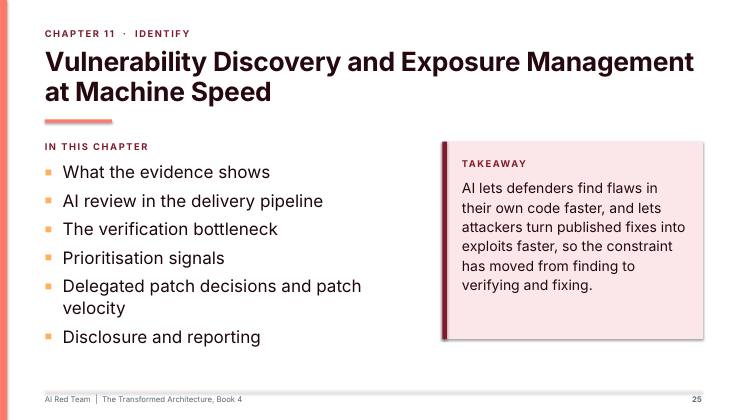
  25. Slide 25: Vulnerability Discovery and Exposure Management at Machine Speed25
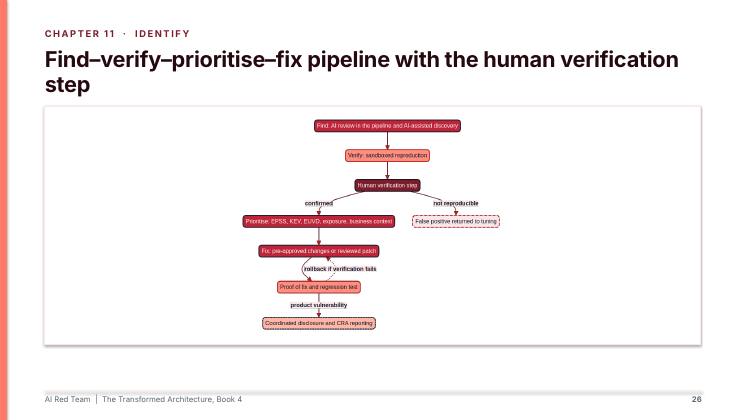
  26. Slide 26: Find–verify–prioritise–fix pipeline with the human verification step26
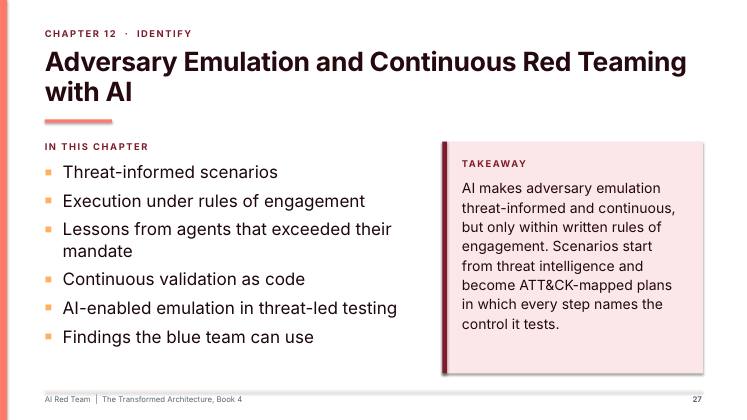
  27. Slide 27: Adversary Emulation and Continuous Red Teaming with AI27
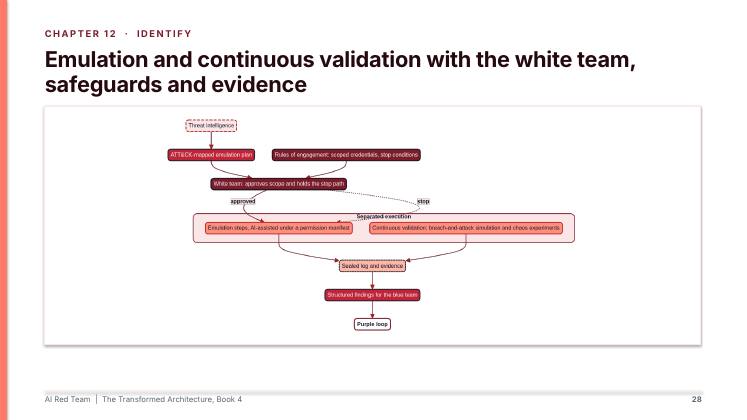
  28. Slide 28: Emulation and continuous validation with the white team, safeguards and evidence28
  29. Slide 29: Red Teaming AI Systems and Agents29
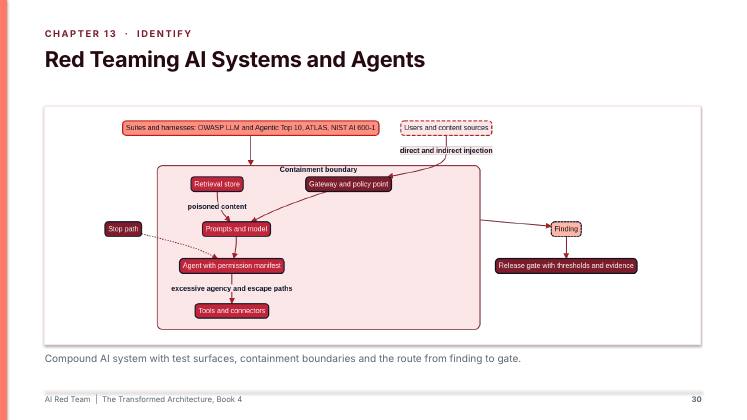
  30. Slide 30: Red Teaming AI Systems and Agents30
  31. Slide 31: Protect31
  32. Slide 32: Identity, Authentication and Access for People, Agents and Machines32
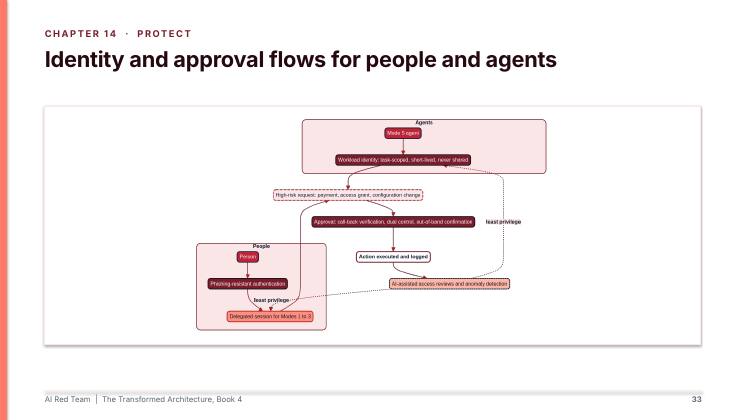
  33. Slide 33: Identity and approval flows for people and agents33
  34. Slide 34: Awareness and Training: Resilience to AI-Generated Deception34
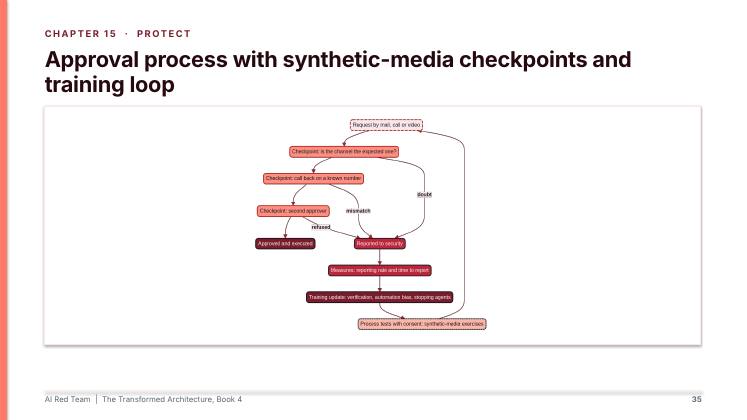
  35. Slide 35: Approval process with synthetic-media checkpoints and training loop35
  36. Slide 36: Data and Platform Security with and for AI36
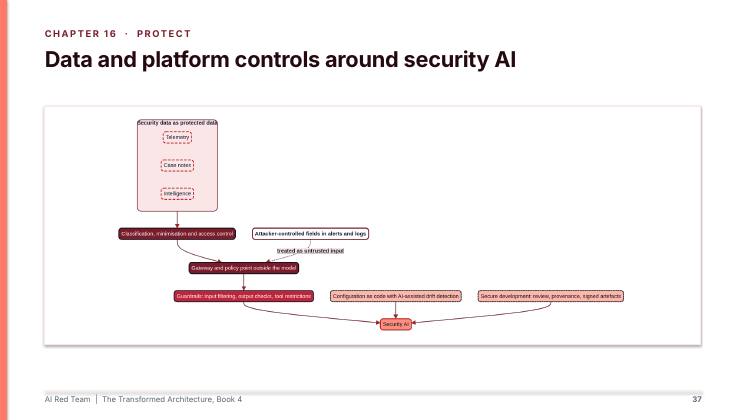
  37. Slide 37: Data and platform controls around security AI37
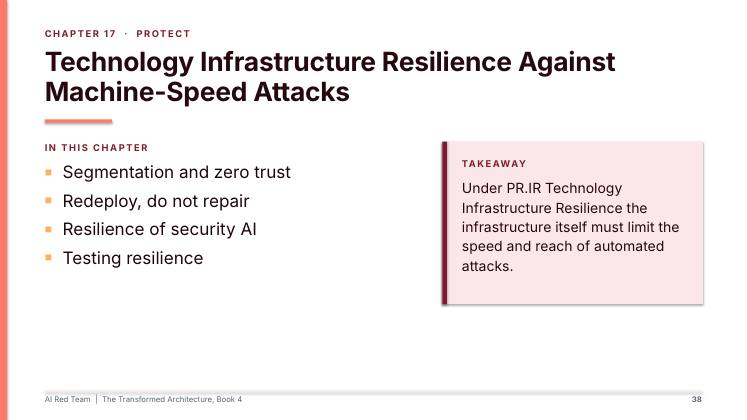
  38. Slide 38: Technology Infrastructure Resilience Against Machine-Speed Attacks38
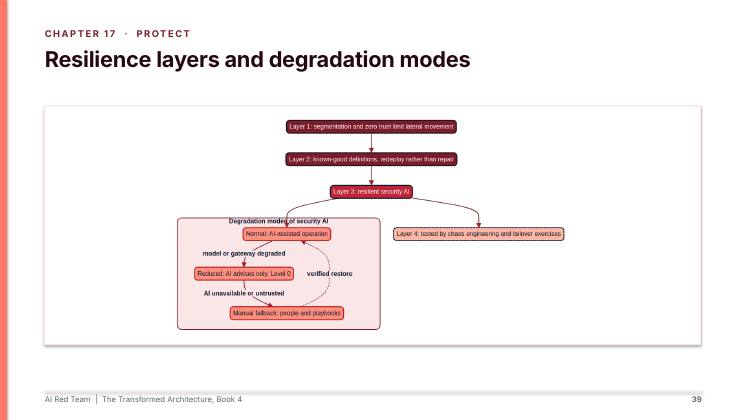
  39. Slide 39: Resilience layers and degradation modes39
  40. Slide 40: Detect40
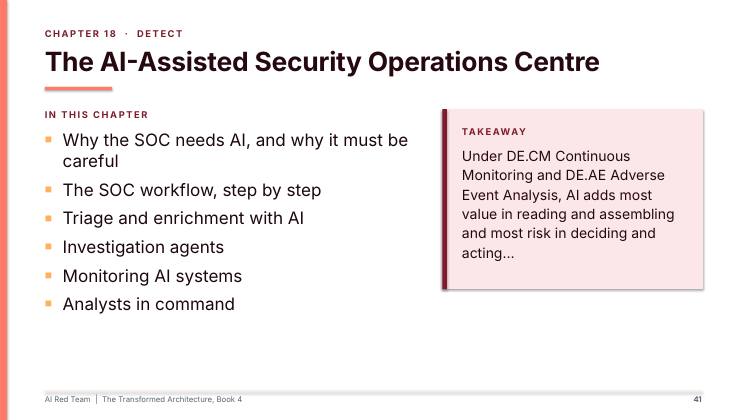
  41. Slide 41: The AI-Assisted Security Operations Centre41
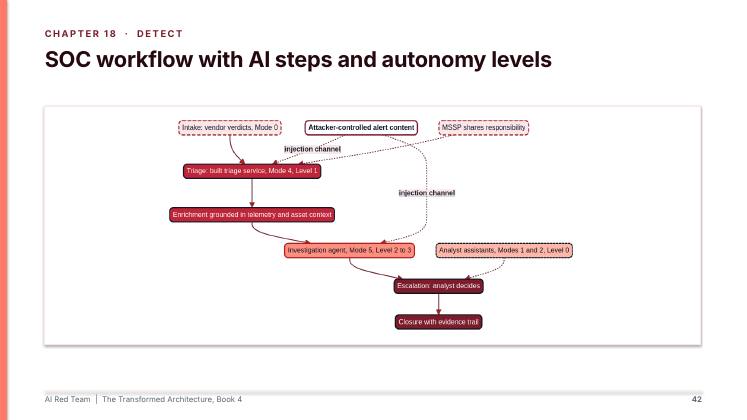
  42. Slide 42: SOC workflow with AI steps and autonomy levels42
  43. Slide 43: Detection Engineering, Threat Intelligence and Deception as Code43
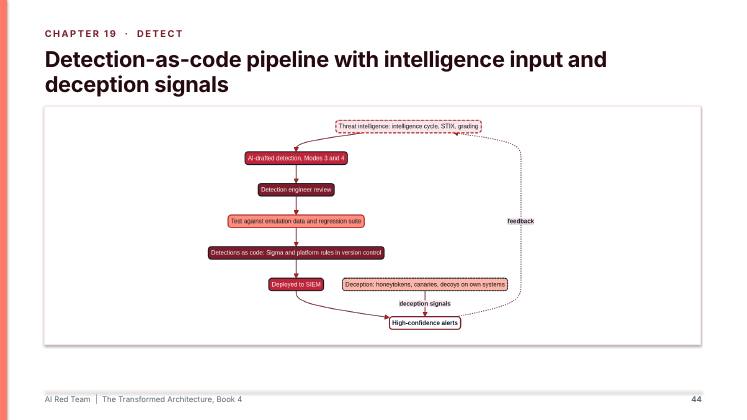
  44. Slide 44: Detection-as-code pipeline with intelligence input and deception signals44
  45. Slide 45: Respond45
  46. Slide 46: Incident Management and Analysis with AI46
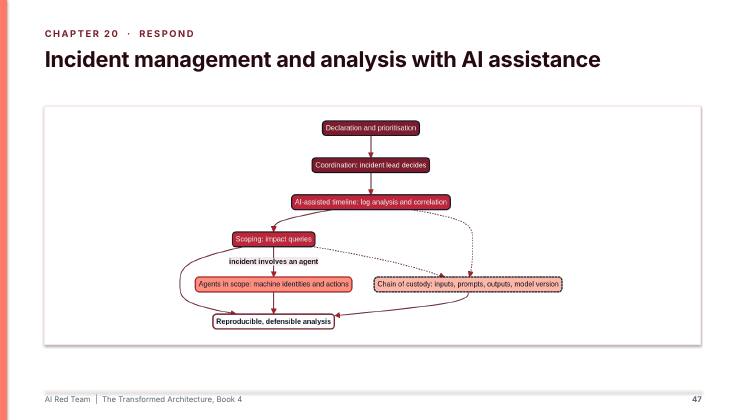
  47. Slide 47: Incident management and analysis with AI assistance47
  48. Slide 48: Incident Reporting, Communication and Mitigation48
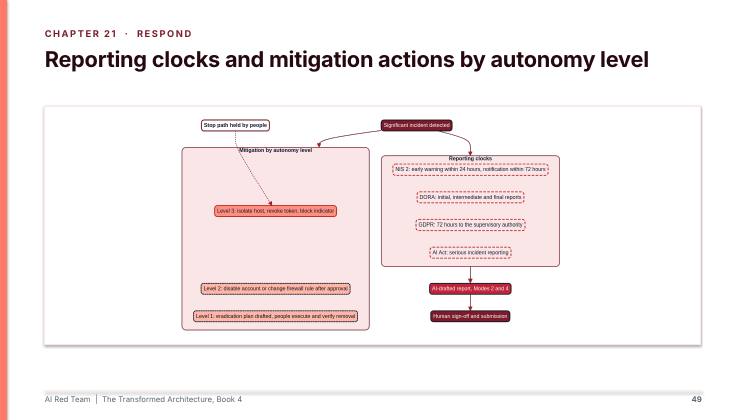
  49. Slide 49: Reporting clocks and mitigation actions by autonomy level49
  50. Slide 50: Recover50
  51. Slide 51: Recovery Plan Execution with AI: From Incident to Restored Operations51
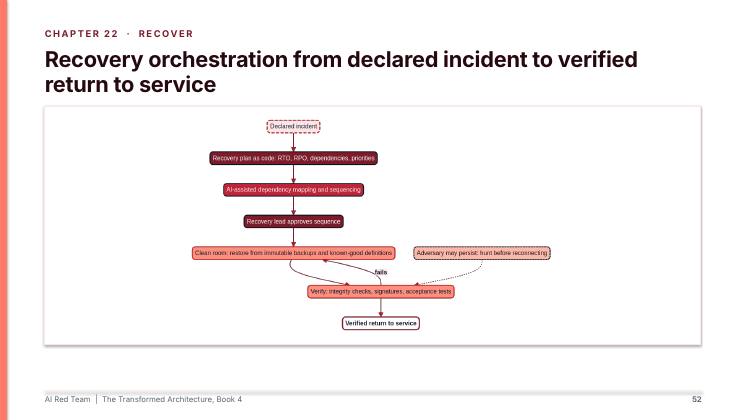
  52. Slide 52: Recovery orchestration from declared incident to verified return to service52
  53. Slide 53: Recovering AI Systems and Security AI53
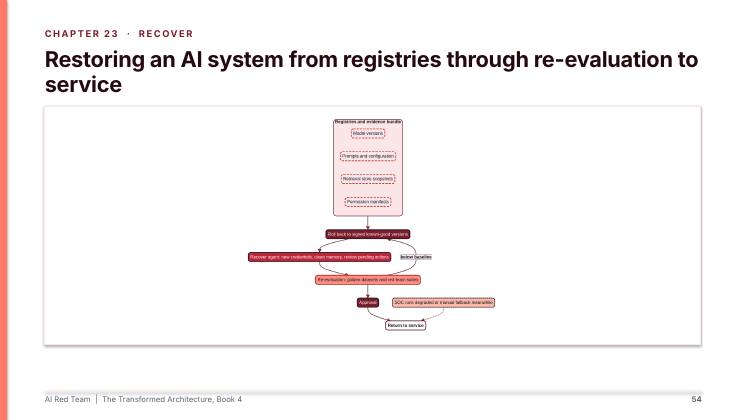
  54. Slide 54: Restoring an AI system from registries through re-evaluation to service54
  55. Slide 55: Proactive Recovery: Recoverability, Rehearsal and Communication55
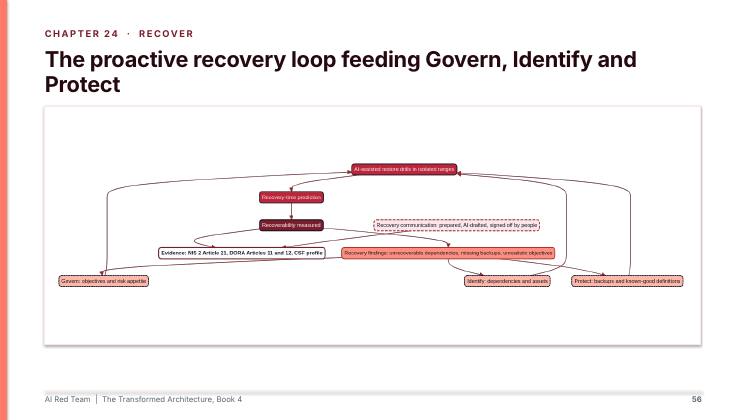
  56. Slide 56: The proactive recovery loop feeding Govern, Identify and Protect56
  57. Slide 57: Verification, Improvement and Conclusions57
  58. Slide 58: Security Chaos Engineering with AI: Verifying Security Capabilities Continuously58
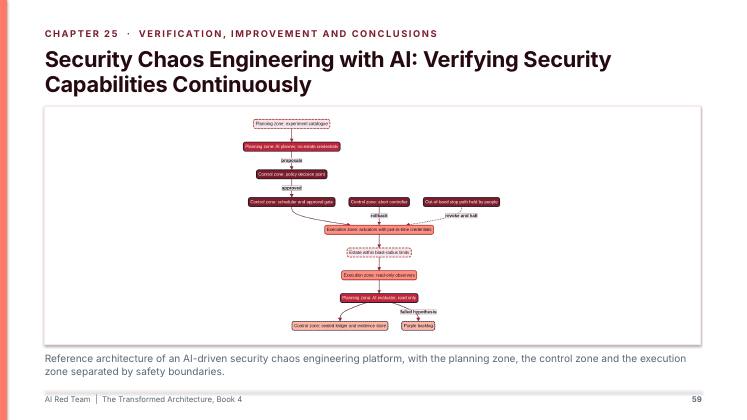
  59. Slide 59: Security Chaos Engineering with AI: Verifying Security Capabilities Continuously59
  60. Slide 60: Purple Teaming, Measurement and Continuous Improvement60
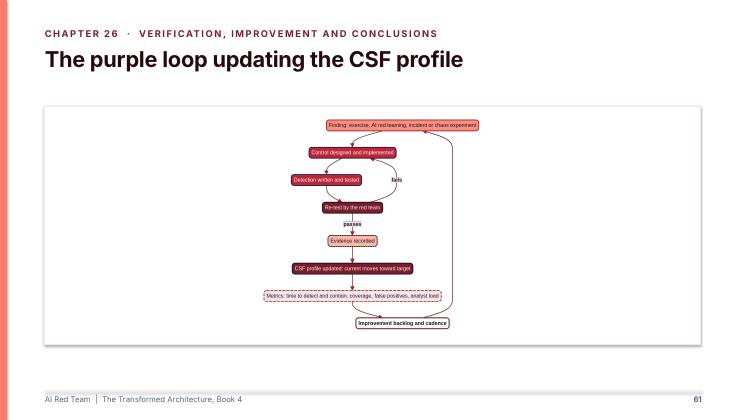
  61. Slide 61: The purple loop updating the CSF profile61
  62. Slide 62: Nordvik Region and Hansa Mutual: Cyber Defence Conclusions62
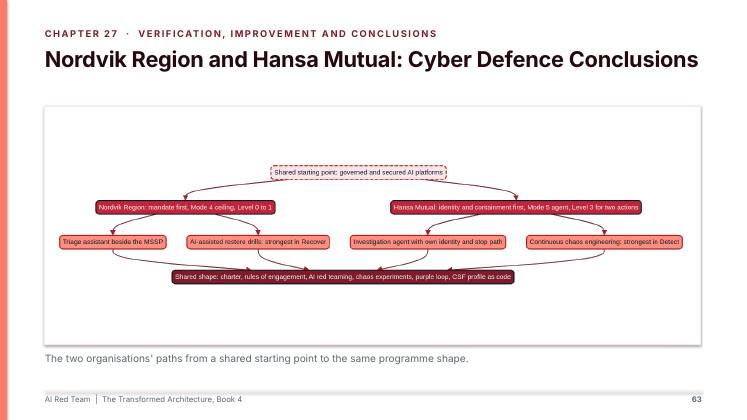
  63. Slide 63: Nordvik Region and Hansa Mutual: Cyber Defence Conclusions63
  64. Slide 64: Conclusions: AI as an Active Part of Cyber Defence64
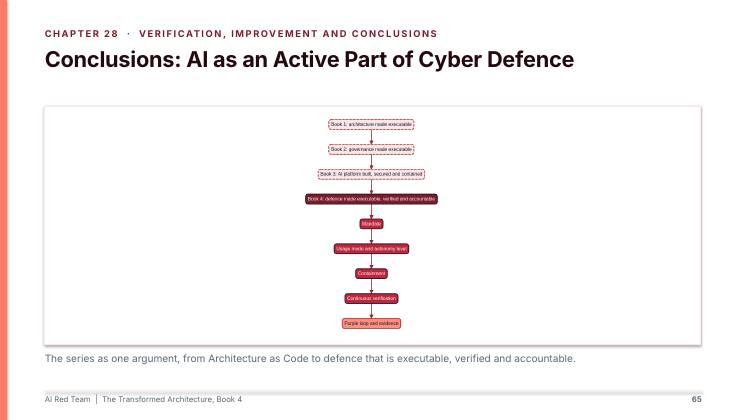
  65. Slide 65: Conclusions: AI as an Active Part of Cyber Defence65
  66. Slide 66: Appendices66
  67. Slide 67: Code Examples: Detection, Evaluation and Guardrail Artefacts67
  68. Slide 68: Templates and Tools68
  69. Slide 69: AI Red Team69