Cover of The Transformed Security Architect

Book 6 · Presentation

The Transformed Security Architect

Role, Craft and Career in the Age of AI in European Enterprises and Public Authorities

65 slidesPowerPoint · 3.9 MB

Download the deck (.pptx) Read the book online

All presentations / The Transformed Security Architect

All slides

Select a slide to see it larger; use the arrow keys to move through the deck.
  1. Slide 1: The Transformed Security Architect1
  2. Slide 2: The Role in Question2
  3. Slide 3: Introduction: The Security Architect Transformed3
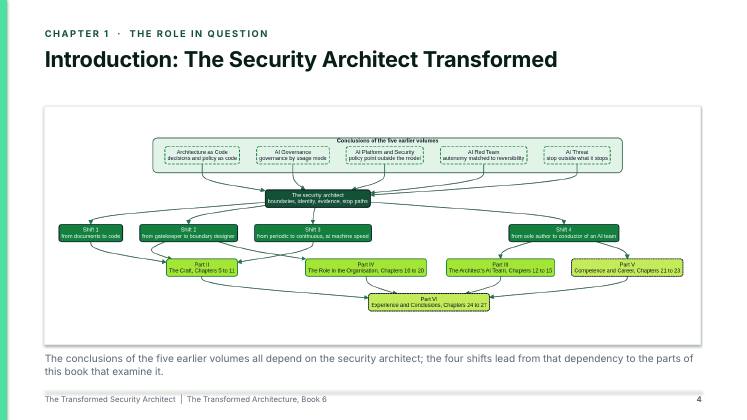
  4. Slide 4: Introduction: The Security Architect Transformed4
  5. Slide 5: What the Security Architect Did: The Role Before the Transformation5
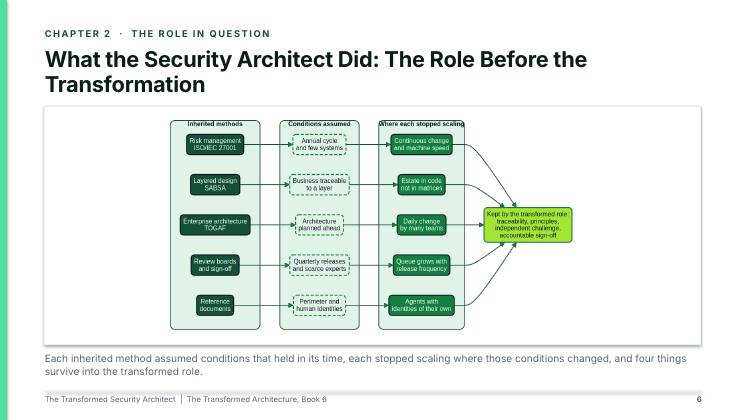
  6. Slide 6: What the Security Architect Did: The Role Before the Transformation6
  7. Slide 7: Four Shifts: Code, Boundaries, Machine Speed and the AI Team7
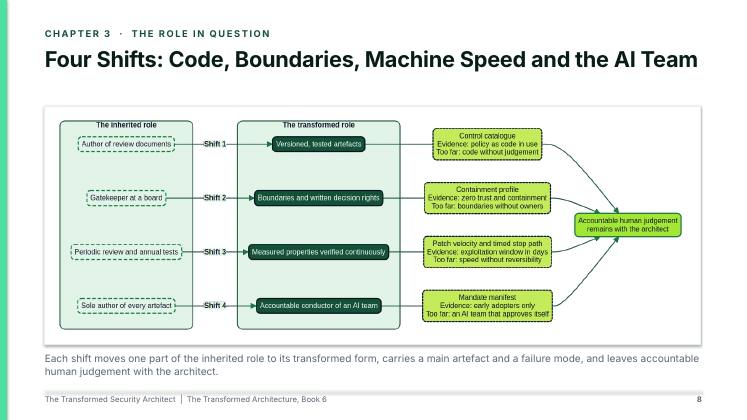
  8. Slide 8: Four Shifts: Code, Boundaries, Machine Speed and the AI Team8
  9. Slide 9: The Transformed Role Defined: Mandate, Accountabilities and Decision Rights9
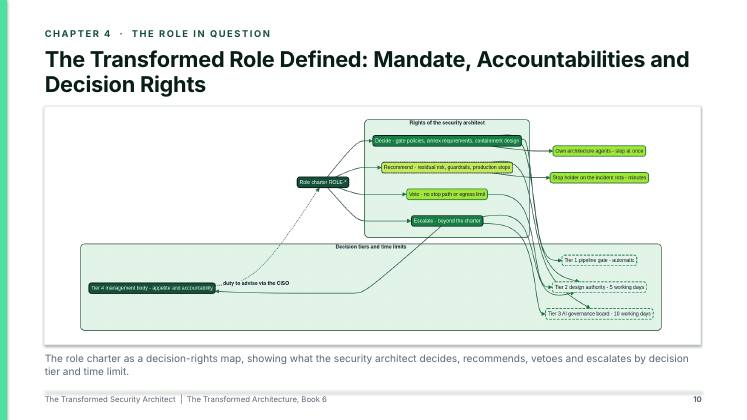
  10. Slide 10: The Transformed Role Defined: Mandate, Accountabilities and Decision Rights10
  11. Slide 11: The Craft11
  12. Slide 12: Security Architecture as Code: From Documents to Executable Design12
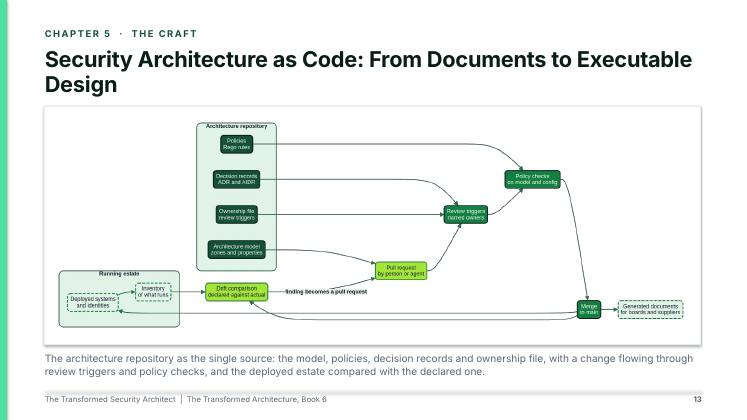
  13. Slide 13: Security Architecture as Code: From Documents to Executable Design13
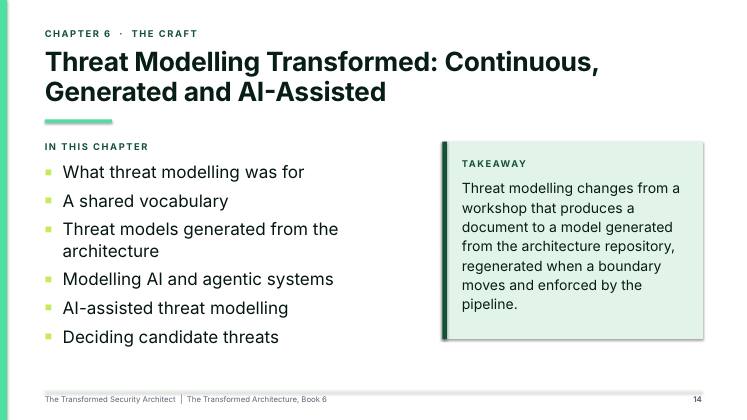
  14. Slide 14: Threat Modelling Transformed: Continuous, Generated and AI-Assisted14
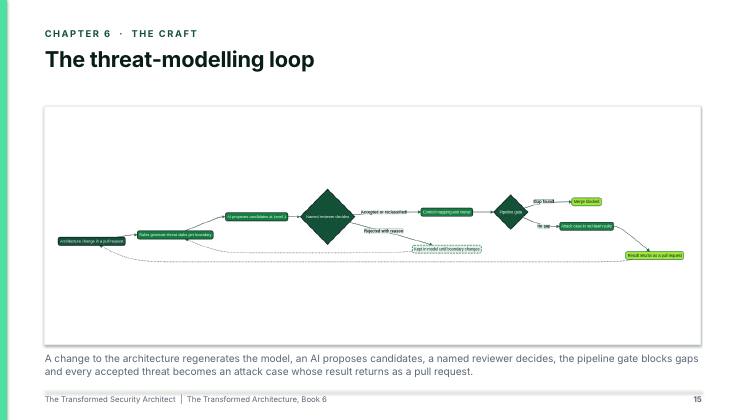
  15. Slide 15: The threat-modelling loop15
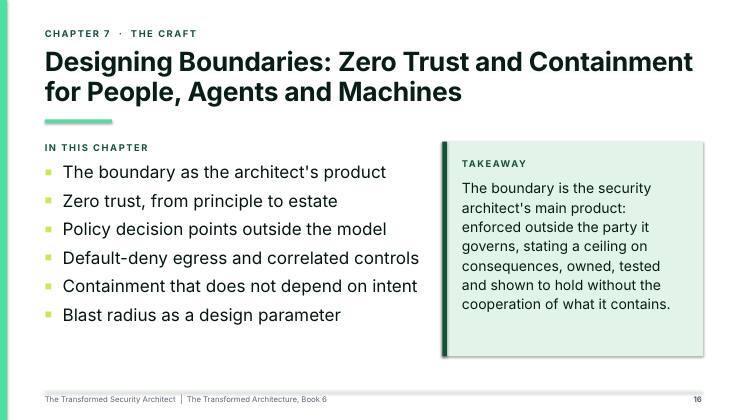
  16. Slide 16: Designing Boundaries: Zero Trust and Containment for People, Agents and Machines16
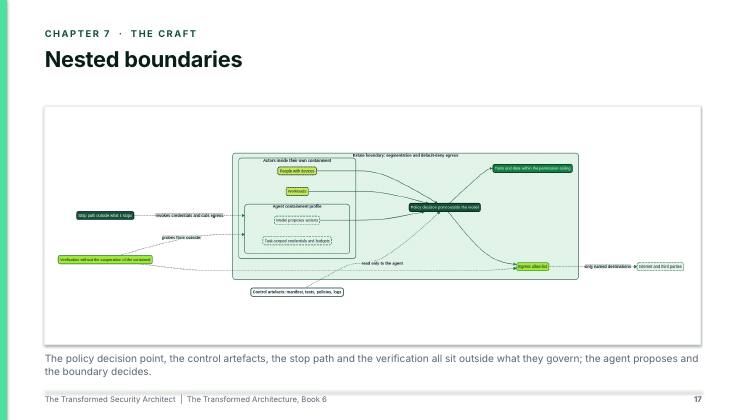
  17. Slide 17: Nested boundaries17
  18. Slide 18: Identity Architecture for Non-Human Actors: Workloads, Agents and Delegated Authority18
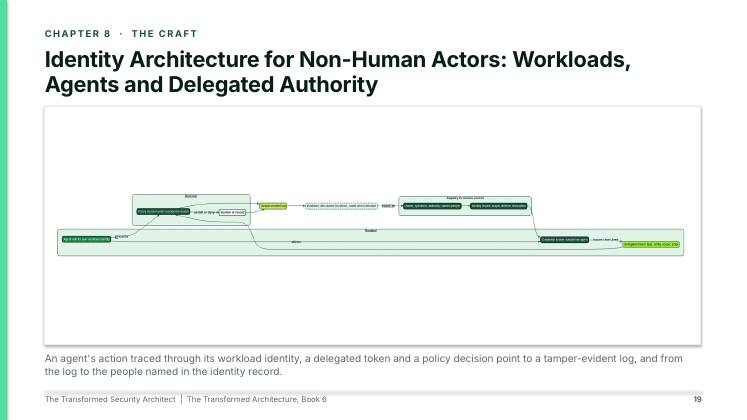
  19. Slide 19: Identity Architecture for Non-Human Actors: Workloads, Agents and Delegated Authority19
  20. Slide 20: The Control Catalogue, Evidence and Assurance as the Architect's Artefacts20
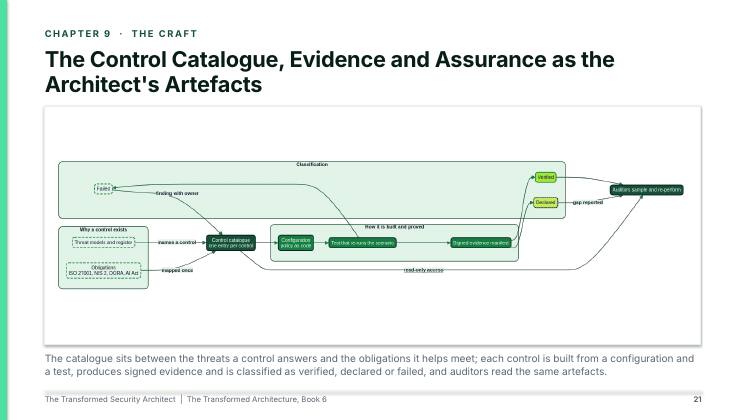
  21. Slide 21: The Control Catalogue, Evidence and Assurance as the Architect's Artefacts21
  22. Slide 22: Architecting at Machine Speed: Patch Velocity, Detection and the Stop Path by Design22
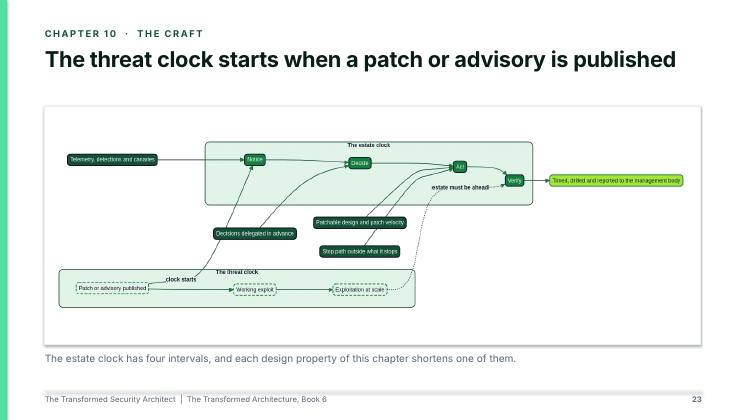
  23. Slide 23: The threat clock starts when a patch or advisory is published23
  24. Slide 24: Resilience and Recovery by Design: The Architect's Share of Recoverability24
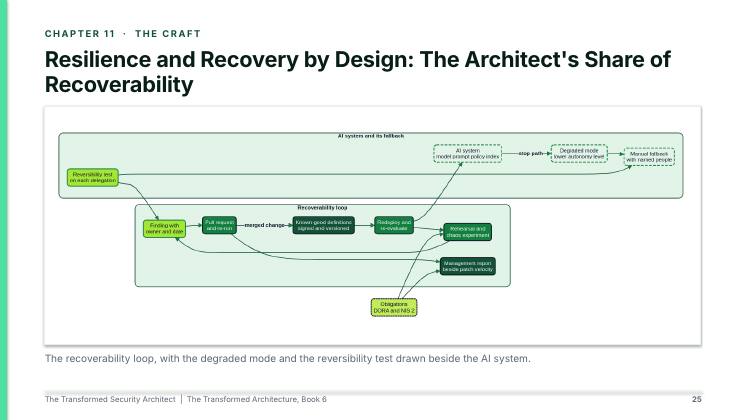
  25. Slide 25: Resilience and Recovery by Design: The Architect's Share of Recoverability25
  26. Slide 26: The Architect's AI Team26
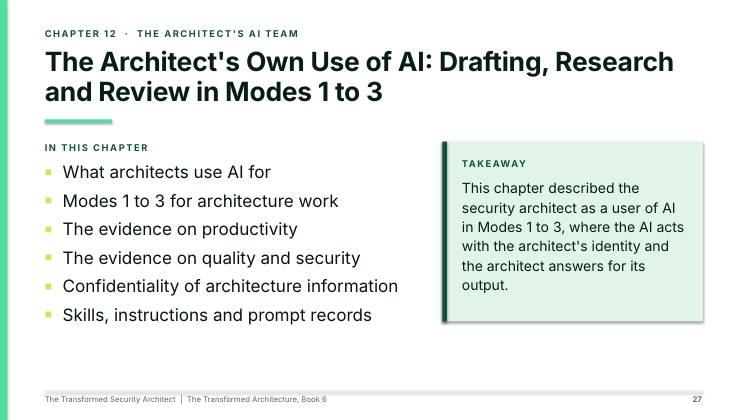
  27. Slide 27: The Architect's Own Use of AI: Drafting, Research and Review in Modes 1 to 327
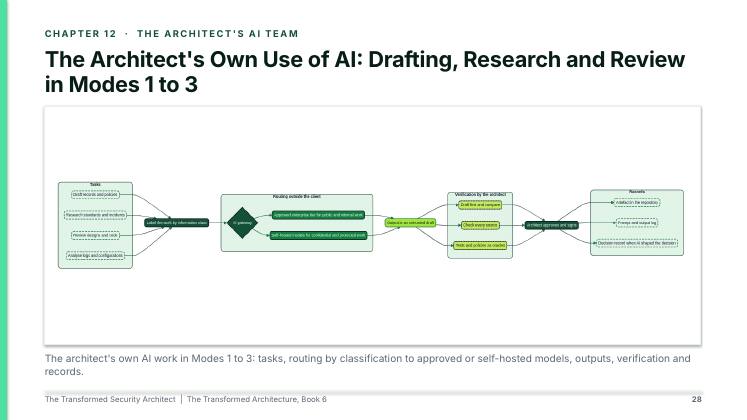
  28. Slide 28: The Architect's Own Use of AI: Drafting, Research and Review in Modes 1 to 328
  29. Slide 29: An AI Agent Team for Security Architecture: Skills, Mandates and Containment29
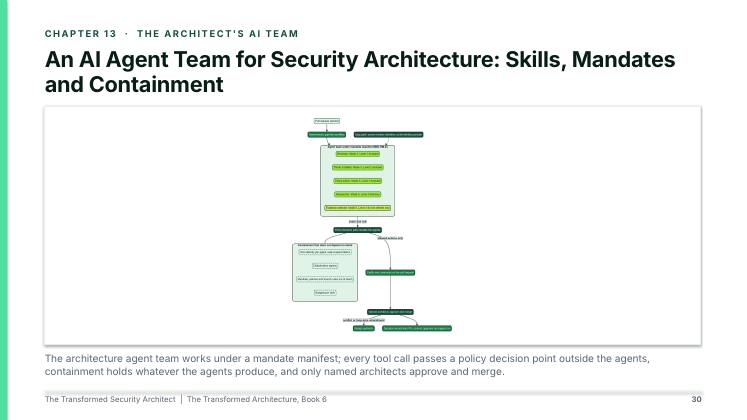
  30. Slide 30: An AI Agent Team for Security Architecture: Skills, Mandates and Containment30
  31. Slide 31: Verifying What AI Proposes: Review for Soundness When the Reviewer Depends on the AI31
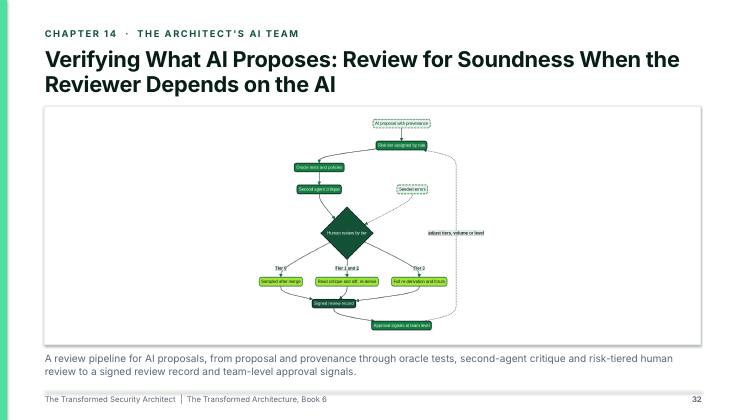
  32. Slide 32: Verifying What AI Proposes: Review for Soundness When the Reviewer Depends on the AI32
  33. Slide 33: Keeping the Craft: Deskilling, Judgement and the Architect Who Still Can33
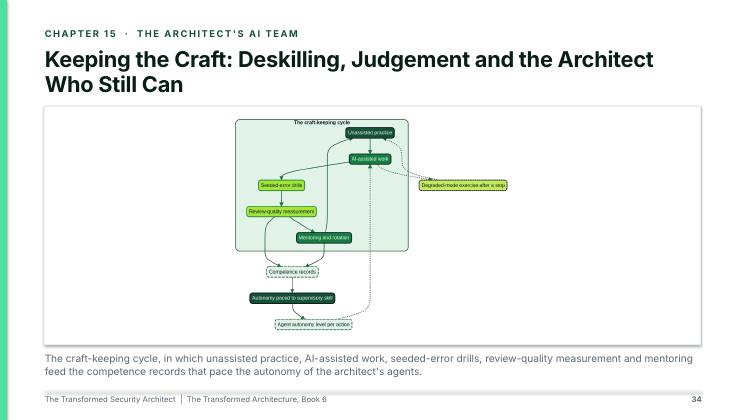
  34. Slide 34: Keeping the Craft: Deskilling, Judgement and the Architect Who Still Can34
  35. Slide 35: The Role in the Organisation35
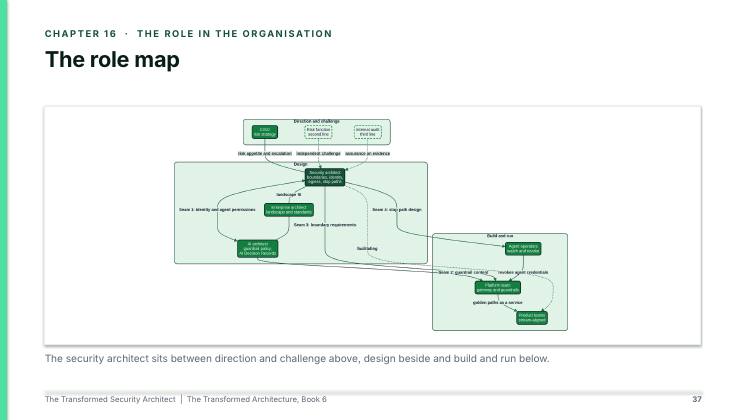
  36. Slide 36: The Role Map: CISO, Enterprise Architect, AI Architect, Platform and Product Teams36
  37. Slide 37: The role map37
  38. Slide 38: Design Authority, Decision Forums and Gates Instead of Meetings38
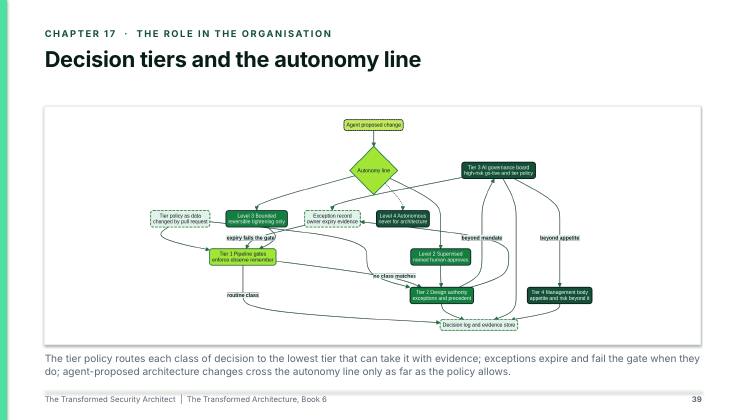
  39. Slide 39: Decision tiers and the autonomy line39
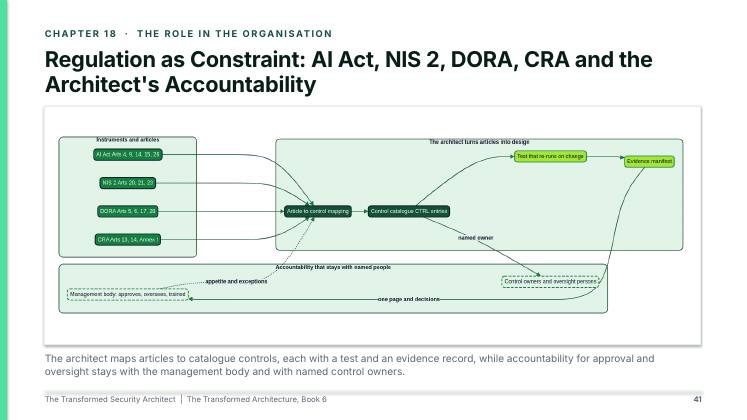
  40. Slide 40: Regulation as Constraint: AI Act, NIS 2, DORA, CRA and the Architect's Accountability40
  41. Slide 41: Regulation as Constraint: AI Act, NIS 2, DORA, CRA and the Architect's Accountability41
  42. Slide 42: Communicating Security Architecture: Boards, Supervisors, Auditors and Engineers42
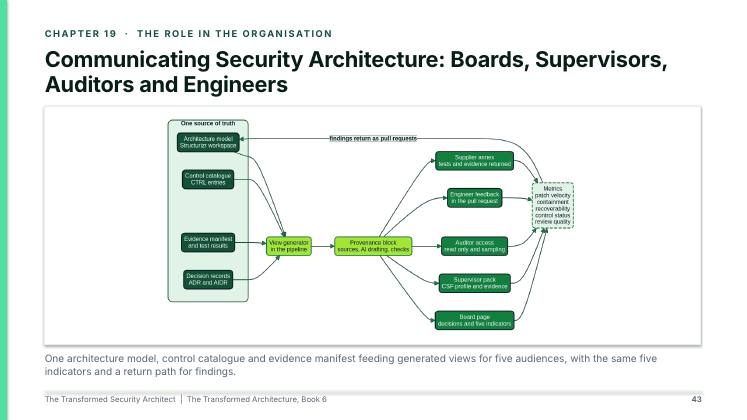
  43. Slide 43: Communicating Security Architecture: Boards, Supervisors, Auditors and Engineers43
  44. Slide 44: Public Authorities and Multinationals: Sovereignty, Procurement and Many Legal Regimes44
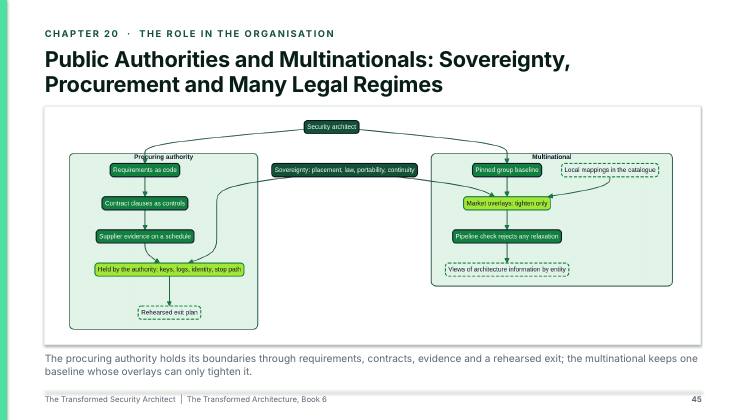
  45. Slide 45: Public Authorities and Multinationals: Sovereignty, Procurement and Many Legal Regimes45
  46. Slide 46: Competence and Career46
  47. Slide 47: Competences of the Transformed Security Architect: A Framework47
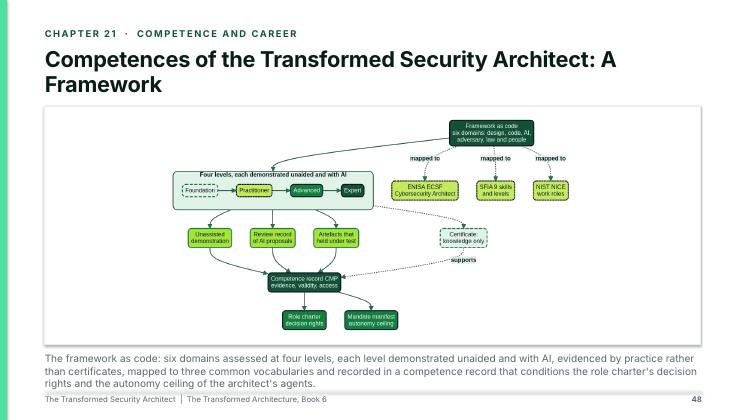
  48. Slide 48: Competences of the Transformed Security Architect: A Framework48
  49. Slide 49: Learning Paths, Certification, Hiring and Upskilling49
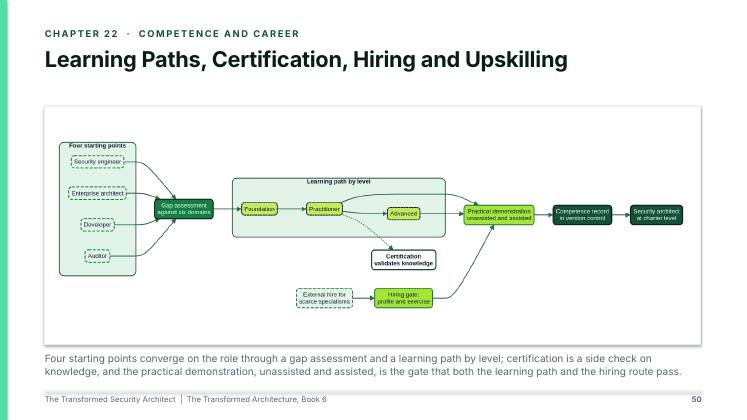
  50. Slide 50: Learning Paths, Certification, Hiring and Upskilling50
  51. Slide 51: The Future of the Role: Will There Be a Security Architect in 2036?51
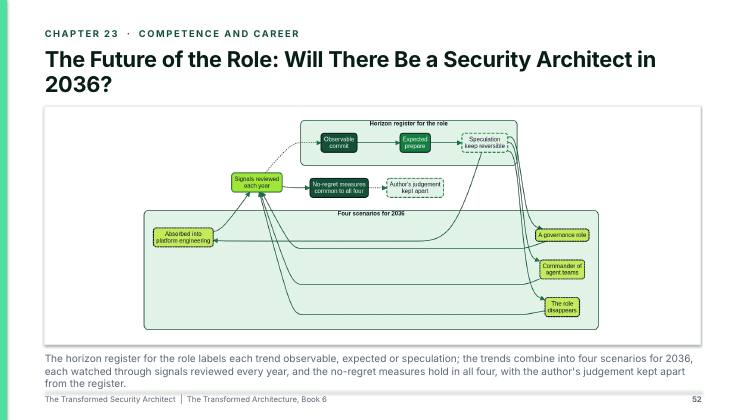
  52. Slide 52: The Future of the Role: Will There Be a Security Architect in 2036?52
  53. Slide 53: Experience and Conclusions53
  54. Slide 54: Case Studies and Anti-Patterns54
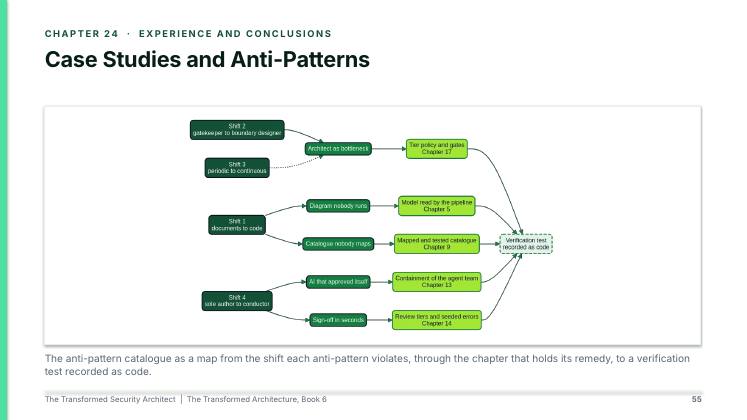
  55. Slide 55: Case Studies and Anti-Patterns55
  56. Slide 56: A Year in the Role: The Transformed Architect at Nordvik Region and Hansa Mutual56
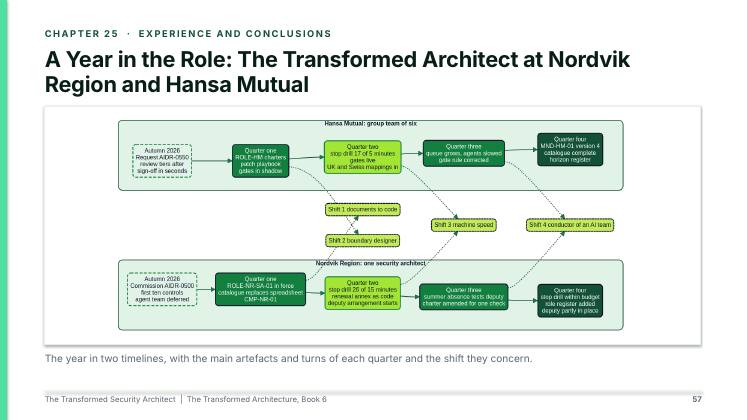
  57. Slide 57: A Year in the Role: The Transformed Architect at Nordvik Region and Hansa Mutual57
  58. Slide 58: Nordvik Region and Hansa Mutual: Conclusions for Two Organisations58
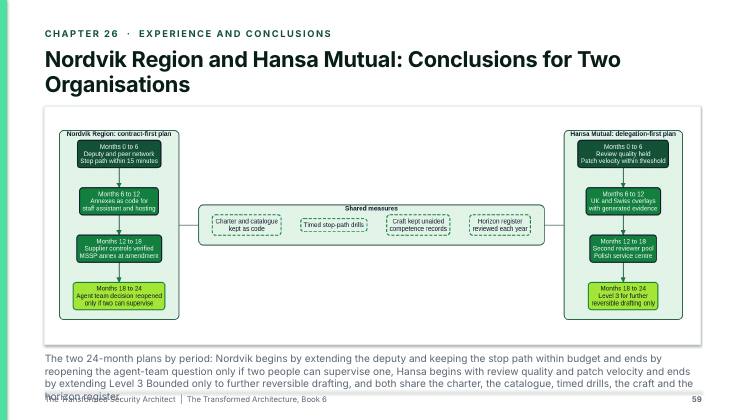
  59. Slide 59: Nordvik Region and Hansa Mutual: Conclusions for Two Organisations59
  60. Slide 60: Conclusions: The Transformed Security Architect60
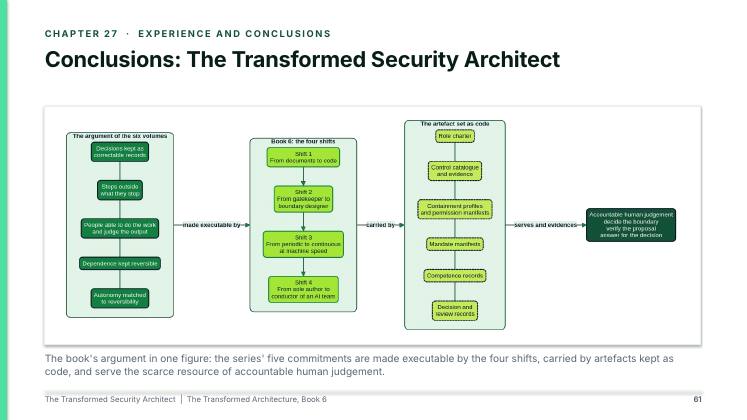
  61. Slide 61: Conclusions: The Transformed Security Architect61
  62. Slide 62: Appendices62
  63. Slide 63: Code Examples: Role, Control and Mandate Artefacts63
  64. Slide 64: Templates and Tools64
  65. Slide 65: The Transformed Security Architect65